What Vendor Policies Should a Dental Office Review in Microsoft 365?
Use this Microsoft 365 vendor policy review checklist for dental offices to tier vendors, collect evidence, and document HIPAA due diligence.
Practical guidance on HIPAA privacy and security rule safeguards for covered entities and business associates.
Need help putting this into practice? See our HIPAA compliance services or the HIPAA handbook.
Use this Microsoft 365 vendor policy review checklist for dental offices to tier vendors, collect evidence, and document HIPAA due diligence.
Use google cloud kpis for health plan data protection to prove encryption, access, backups, monitoring, and incident reporting are working.
Use subcontractor contract clauses for ePHI workstations to require HIPAA-aligned use rules, physical safeguards, evidence, audit access, and termination.
This shared Chromebook ePHI incident postmortem explains how an unsecured signed-in session exposed patient data and how to prevent recurrence.
Use an audit log kpis monthly compliance report to show HIPAA log coverage, review completion, alert response, retention, and control gaps.
Learn hipaa physical access requirements google workspace devices: protect offices, endpoints, visitors, and emergency access under HIPAA.
HIPAA device and media control requirements Microsoft 365: govern ePHI devices, removal, disposal, reuse, movement records, and backups.
Understand audit log requirements for patient records under HIPAA 164.312(b), including what to log, who is covered, and practical evidence of compliance.
This email TLS for patient data ultimate guide explains HIPAA transmission security, implementation evidence, a testing checklist, and audit FAQs.
Single breach vs pattern vendor cure plan: HIPAA requires action when a known pattern creates material vendor contract violations.
Learn how to set up continuous microsoft 365 security alerts with prioritized telemetry, Sentinel queries, tuning, and incident response workflows.
Learn to require https for phi azure app service with HTTPS Only, TLS 1.2, validation, and HIPAA evidence in 30 minutes.
Run a hipaa shared clinic pc badge login migration in 30 days with a phased plan, rollback controls, and evidence for HIPAA workstation security.
Learn how to move from untracked USBs to a check-out log with a phased HIPAA-ready process for inventory, custody, encryption, and validation.
Use a focused amendment package to add ephi safeguards to group health plan documents and create assessment-ready evidence in 60 minutes.
Avoid hipaa documentation mistakes sharepoint teams make: retain, secure, update, and make HIPAA records available for six years.
Use this healthcare written policy requirements quick start to create, approve, store, and assign HIPAA documentation in four hours.
A microsoft 365 device control board report shows device custody, data-removal, backup, and exception risk under HIPAA.
A workstation security migration plan for ehr clinics moves devices to authorized-only EHR access with staged safeguards, testing, and evidence.
Calculate the roi of security policy software for a 10 person clinic by comparing subscription, labor, training, audit costs, and avoided risk.
A policy documentation maturity rubric SharePoint teams can use to score, evidence, and improve HIPAA policy governance from ad hoc to optimized.
A hipaa workstation tabletop exercise for front desks tests how staff protect ePHI when privacy, visitors, and interruptions collide.
Business associate breach cure evidence google cloud: collect dated, immutable proof that a vendor remediated a material HIPAA contract violation.
Business associate breach escalation evidence includes dated notices, receipt records, investigation decisions, cure actions, and retained Microsoft 365 audit logs.
Learn what facility access control aws dental office means under HIPAA, who must follow it, and the records an assessor expects to see.
See which baa clauses protect ehr records from improper changes, including flow-down, audit, and termination language for HIPAA vendors.
Learn the written policy requirements for compliance teams under HIPAA: document Security Rule policies, records, access, reviews, and retention.
Learn the server room access requirements for healthcare offices, including HIPAA roles, visitors, emergency entry, logs, and maintenance records.
HIPAA EHR audit log requirements require organizations to record and examine activity in systems that create, receive, maintain, or transmit ePHI.
hipaa business associate breach requirements azure require contracts, incident reporting, cure actions, and termination or HHS reporting for material violations.
This hipaa ehr user authentication guide explains how to verify EHR users, deploy MFA, document evidence, and pass a HIPAA review.
Compare hipaa incident management software pricing jira servicenow by clinic size: Jira fits lean teams; ServiceNow fits governed enterprises.
Compare intune vs jumpcloud hipaa workstation pricing by clinic size, including practical tiers, tradeoffs, and policy evidence needs.
Configure google drive sharing settings for plan ephi with a restricted Workspace unit, no external sharing, audit evidence, and access controls.
Learn how to set azure rbac roles in access control iam with least-privilege group assignments, verification, and HIPAA-ready evidence.
Use this written policy tabletop exercise facilitator guide to test policy access, retention, updates, and evidence capture in 90 minutes.
Learn to report policy documentation to board quarterly with clear risk, retention, access, and change metrics that support HIPAA oversight.
Choose cloud entra id vs on-prem active directory patient data access based on EHR, devices, and off-site needs while documenting HIPAA authorization.
Backup vs disaster recovery patient records: HIPAA requires retrievable copies, procedures to restore lost data, and plans to protect care operations.
Use noncompliant vendor contract compliance steps to cure BAA gaps, validate safeguards, preserve leverage, and document HIPAA-ready vendor oversight.
Map iso 27001 controls for hipaa laptop inventory to HIPAA, SOC 2, and NIST CSF with evidence that reduces duplicate audit work.
Use this dental office security policies checklist to document the first HIPAA Security Rule policies in two focused hours.
Use kpis for tracking PHI device movement in a clinic to prove documented custody, backup, secure reuse, and disposal during an EHR migration.
Use a business associate breach maturity assessment to score oversight from ad hoc contracts to optimized detection, cure, and termination decisions.
A hipaa ehr access control ultimate guide for limiting EHR access, documenting safeguards, and funding HIPAA-ready workflows.
Learn what is a security official in google workspace and how a healthcare practice can document HIPAA Security Rule accountability.
Learn when a business associate agreement cloud backup vendor is required, what HIPAA terms it needs, and what proof buyers expect.
SharePoint version history audit evidence shows auditors who changed ePHI, when prior copies were preserved, and how integrity controls are tested.
The workstation security cost per clinic typically runs $500–$1,100 per worker in year one; see a 50-person budget, ROI, and breakeven math.
Use a hipaa annual subcontractor security review clause to require documented yearly reviews, evidence, audit access, and remediation rights.
Establish minimum identity checks for health records in two hours with HIPAA §164.312(d) evidence an auditor can test.
Understand hipaa email requirements microsoft 365: secure patient data in transit, apply encryption when appropriate, and document safeguards.
terraform s3 versioning hipaa integrity helps preserve recoverable ePHI copies and detect improper deletion through repeatable infrastructure controls.
Understand hipaa workstation security requirements under 164.310(c), with remote-work safeguards, implementation steps, a checklist, and FAQs.
Compare onetrust vs logicgate vendor breach pricing tiers, size fit, and evidence workflows for HIPAA business-associate breach response.
Learn how to set ChromeOS screen lock Google Admin console settings to require timely locking and password-protected access on managed devices.
Run a stolen EHR badge tabletop exercise to test identity verification, revoke access, preserve evidence, and improve HIPAA response decisions.
Learn how to report Google Workspace policy changes to board members with clear risk, trend, and compliance evidence.
Learn how to fix shared Dentrix logins audit finding with unique accounts, access cleanup, evidence, and repeatable HIPAA controls.
Learn how to fix overbroad google cloud iam roles audit finding with scoped replacements, validation evidence, and repeatable review controls.
Use this ehr login verification policy template to document seven HIPAA-aligned clauses for verifying every EHR user and entity.
Do 5-person clinics need a security policy binder? Yes—but it should be a practical, documented set of HIPAA policies, not a generic manual.
Avoid microsoft 365 audit log mistakes by enabling complete logging, retaining evidence, reviewing alerts, and documenting audit controls.
Avoid group health plan document mistakes sponsor ePHI: seven fixes for sponsor access, safeguards, vendors, and incident reporting.
An ehr access control policy template should define who receives EHR access, how it is approved, reviewed, removed, and audited under HIPAA.
Use business associate rfp template questions to assess safeguards, subcontractors, incident response, and contract readiness before vendor selection.
Collect hipaa audit documents sharepoint evidence for policies, risk actions, access reviews, training, change records, and retention proof.
Understand plan sponsor safeguard requirements for Azure EPHI: plan document duties, separation, Azure evidence, and incident reporting.
Build a powershell business associate cure deadline tracker that calculates cure dates, flags escalation windows, and preserves review evidence.
Compare splunk vs datadog hipaa audit log pricing for a 200-user firm, including cost drivers, retention, BAA fit, and alternatives.
Set a 5-minute intune device lock auto-lock timer clinic pcs policy in Microsoft Intune and document HIPAA-ready proof of enforcement.
Learn how to fix missing ephi clause after plan audit with a targeted plan amendment, evidence file, and HIPAA control validation.
Build a hipaa nurse workstation training plan with role-based lessons, practical checks, and audit-ready evidence for ePHI workstation use.
hipaa business associate breach vs violation: distinguish a curable contract breach from an ongoing violation and document the required response.
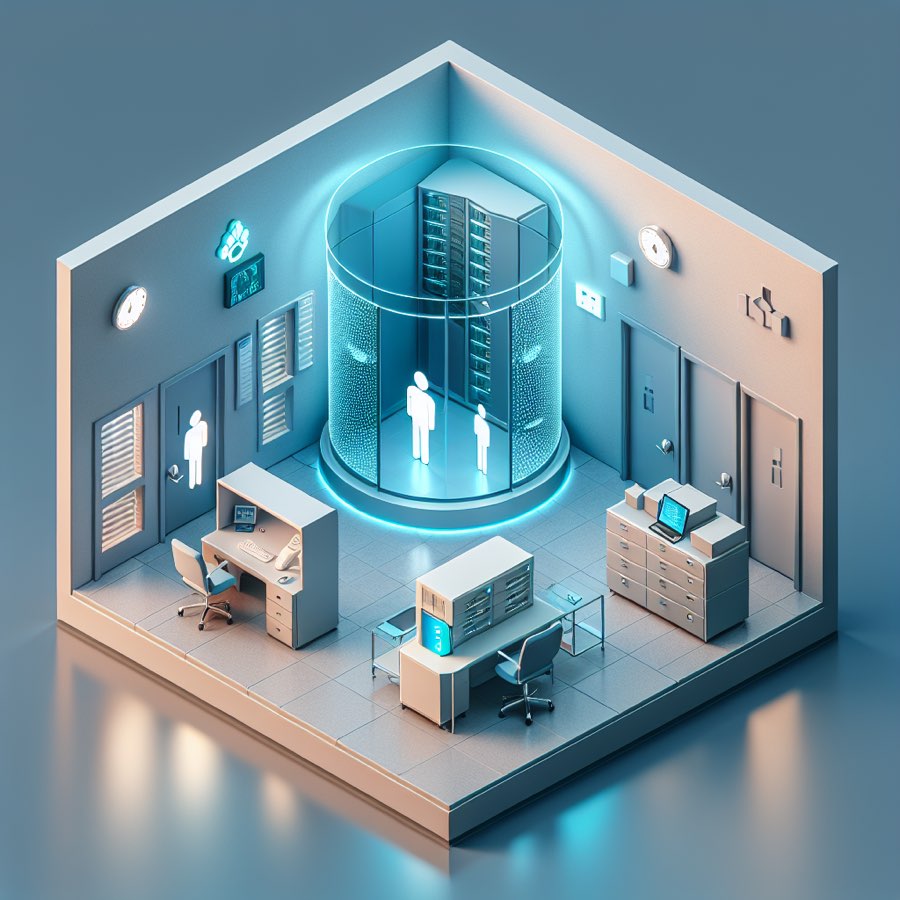
A practical, step-by-step guide to implementing HIPAA Facility Access Controls (164.310(a)(1)) with actionable technical controls, policies, and small-business examples to meet HIPAA requirements.
Step-by-step guidance for building audit-ready HIPAA 164.316(a) policies and procedures within your HIPAA — templates, evidence, and change control best practices.
Step-by-step guidance for creating, documenting, and maintaining HIPAA-compliant written policies and procedures to meet 164.316(b)(1) and demonstrate ongoing HIPAA conformance.
Michigan healthcare provider, Oakwood Healthcare, Inc., has verified that an employee at Oakwood Hospital & Medical Center had their employment terminated for posting derogatory remarks about a patient on their Facebook page, leading to a HIPAA privacy violation
Understanding HIPAA is crucial for Managed Service Providers offering services to the healthcare sector or to organizations that assist the healthcare industry
Having a disaster recovery plan for HIPAA is crucial when it comes to contingency planning
Password sharing in healthcare may contribute to productivity in certain situations, however, it is crucial to maintain strict control over this practice and never allow it for accessing electronic protected health information (ePHI), a HIPAA violation.
Our Free HIPAA Release Form for Texas serves as a means to request medical records while ensuring compliance with the regulations outlined in the Health Insurance Portability and Accountability Act (HIPAA).
Our Free HIPAA Release Form for Florida serves as a means to request medical records while ensuring compliance with the regulations outlined in the Health Insurance Portability and Accountability Act (HIPAA).
Our Free HIPAA Release Form for California serves as a means to request medical records while ensuring compliance with the regulations outlined in the Health Insurance Portability and Accountability Act (HIPAA).
Medical centers must comply with the Administrative Simplification standards of HIPAA in order to be HIPAA compliant.
The correlation between HIPAA compliance in urgent care is not seamless, due to the potential for heightened emotions during emergency events.
To become HIPAA compliant, a Covered Entity or Business Associate need to understand the responsibilities of a HIPAA Compliance Officer. It is crucial to note that a HIPAA Compliance Officer is entrusted with two distinct roles that of a Privacy Officer and a Security Officer.
Covered entities and business associates are obligated to implement various safeguards to ensure compliance with the standards for HIPAA email regulations.
In order to safeguard sensitive patient information stored in the cloud, healthcare organizations are required to opt for hosting companies that comply with HIPAA regulations when hosting applications, websites, and databases.
Text message (SMS) regulations under HIPAA outline the specific circumstances in which communication with a patient via text message (SMS) is permitted, as well as the necessary precautions for all other text messages (SMS).
The primary responsibility of a HIPAA Security Officer is to create and execute guidelines and protocols that safeguard the authenticity of electronic Protected Health Information.
The HIPAA training requirements lean more towards offering guidance rather than enforcing strict laws. They recommend that training should be provided periodically and when specific events take place. We propose implementing a more organized training regimen and adopting best practices for Covered Entities and Business Associates when it comes to HIPAA training.
Everything you need to know about HIPAA; what it is, who it applies to, and more.
Covered Entities and Business Associates must familiarize themselves with the HITECH Act as it closely relates to the HIPAA and HITECH regulations. It is essential to comprehend the similarities and distinctions between HIPAA and HITECH, and where to access further details about these Acts.
A Password Sharing Policy that is compliant with HIPAA should explicitly forbid Covered Entities, Business Associates, and their staff members from sharing passwords that grant access to electronic Protected Health Information (ePHI). Additionally, it is highly recommended to disallow caregivers from using shared passwords to access patient portals.
Safeguarding the security of medical records are required to meet HIPAA compliance requirements, this can be best achieved through cloud services.
Performing a HIPAA risk assessment is crucial for ensuring compliance with HIPAA regulations, discovering potential areas of vulnerability and weakness that could lead to data breaches. Once these areas are identified, Privacy and Security Officers can then create a comprehensive Risk Management Plan and implement necessary measures to effectively safeguard against unauthorized disclosures of Protected Health Information (PHI).
The master guide for HIPAA compliance for all dentists, regardless of whether they are self-contained entities or not.
Everything you need to know about HIPAA encryption requirements
What is a HIPAA Covered Entity? and everything you need to know about them.
The comprehensive HIPAA guide for telemedicine and the proper methods for transmitting electronic protected health information (ePHI) during remote healthcare services
Healthcare organizations must prioritize HIPAA compliance when it comes to their social media policies. It is imperative that patient information remains confidential, protected, and is only shared with explicit consent. To prevent any HIPAA violations, healthcare employees need to create and enforce well-defined social media policies. These guidelines encompass various aspects and serve as a roadmap.
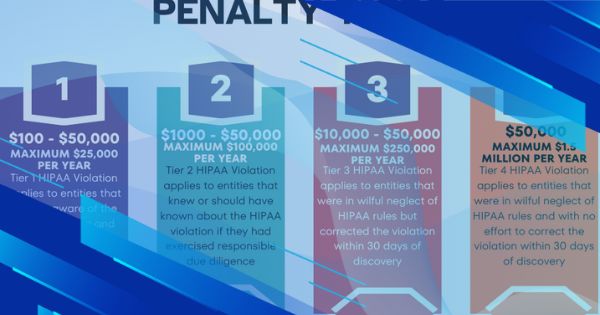
HIPAA violation fines are given by the Department of Health and Human Services Office for Civil Rights (OCR) and state attorneys general to entities that fail to comply with HIPAA regulations.
UnitedHealthcare Settles for $80,000

Talk with our team about your framework, your gaps, and the right plan.
Get a demo