Which Logs Prove Session Authenticity Maturity? (SC.L2-3.13.15)
Use session authenticity maturity evidence logs to score SC.L2-3.13.15 from ad hoc TLS proof to monitored, optimized mutual authentication.
News and guidance on cybersecurity, regulation, and compliance for regulated businesses.
Need help putting this into practice? See our compliance services.
Use session authenticity maturity evidence logs to score SC.L2-3.13.15 from ad hoc TLS proof to monitored, optimized mutual authentication.
offer letter security terms ISO 27001 SOC 2 NIST map employment security clauses to evidence that supports enterprise reviews and audits.
Use these questions to ask a media disposal vendor about destruction methods, chain of custody, evidence, contracts, and ISO 27001 alignment.
Learn what employee acceptable use policy cybersecurity requirements must cover under ECC 2:2024 control 1-9-4, including signed acknowledgments and awareness.
Network security management SIEM log requirements: the events, evidence, and approvals needed to support ECC 2:2024 practice 2-5-3.
What do auditors look for in microsoft 365 event triage? Clear assessment decisions, retained evidence, accountable owners, and incident escalation records.
A google apps script breach postmortem showing how an unapproved OAuth-enabled script exfiltrated files and how to evidence SC.L2-3.13.13.
Vulnerability scans vs penetration tests for small business: start with scheduled scans, then use pen tests to validate high-risk exposure.
Use powershell remove former vendor access workflows to disable accounts, revoke sessions, remove group access, and retain audit evidence.
Learn how using Amazon Macie to find and tag CUI files in S3 supports MP.L2-3.8.4 with discovery, tags, verification, and evidence.
An off-site asset security guide for MSSP analysts: protect client devices and media away from premises with evidence-ready ISO 27001 controls.
Use this defender usb ownership evidence checklist to block unowned removable media and prove MP.L2-3.8.8 compliance with Azure evidence.
cmmc remote worker antivirus scanning requires defined periodic scans and real-time scanning of externally sourced files when downloaded, opened, or executed.
This cmmc password vault guide explains how to protect stored and transmitted passwords for CMMC IA.L2-3.5.10 with evidence-ready steps.
Build a vulnerability management board deck that translates ECC 2-10-3 evidence into business risk, remediation progress, and decisions.
Use this phishing risk policy template for employees to define reporting, training, testing, and evidence for CMMC Level 2 compliance.
Compare okta vs entra id user lifecycle pricing for 50-user saas, including tiers, M&A fit, ISO 27001 lifecycle controls, and alternatives.
Use this Microsoft 365 CUI access policy template to document screening gates before authorizing access to CUI systems under PS.L2-3.9.1.
Compare in-house vs msp maintenance cost, 12-month budgets, risk savings, and breakeven points for MA.L2-3.7.1 maintenance.
Learn to set Google Workspace session length admin console policies, test expiration, and produce SC.L2-3.13.9 evidence for assessors.
Run a test data leak tabletop exercise to validate containment, notification, evidence, and ISO 27001 test-information controls.
Learn to generate employment security clauses with PowerShell using approved templates, HR data, audit logs, and review gates.
How to cloud kms destroy key versions before disk disposal with Google Cloud steps, verification, and ISO 27001 evidence.
Learn how to build an azure asset inventory in 2 hours using Azure Resource Graph, owners, and evidence for ISO 27001 5.9.
Configure Microsoft Bookings secure area visitor approval settings to require staff approval, document sponsor details, and retain visitor records.
Fire suppression vs fire detection server room controls serve different purposes: detect and alert early, then contain or extinguish fire.
Does an information security policy need CEO approval? ISO 27001 requires management approval, not necessarily CEO sign-off.
docusign vs ironclad IP agreement pricing for small teams: DocuSign is cheaper for standard IP signatures; Ironclad suits complex contract workflows.
Cyber incident vs data breach prime contractor reporting: report contractually required incidents, not only confirmed breaches, and document every decision.
Meet cmmc vendor escort requirements with a two-hour baseline: named escorts, restricted temporary access, and maintenance logs an assessor can verify.
Learn whether can google drive store cui with fips encryption, what evidence is needed, and how SC.L2-3.13.11 applies.
API penetration testing scope requirements 2-11-3 explicitly include APIs supporting Internet-facing services under ECC 2:2024.
Use this CMMC unauthorized use assessment checklist to define authorized activity, review evidence, and baseline SI.L2-3.14.7 in three hours.
Avoid nda inventory mistakes before assessments by proving every required signer, agreement, version, and review cycle is complete for ISO 27001 6.6.
Use google cloud identifier reuse board report kpis to show policy coverage, blocked reuse, exceptions, and residual access risk to directors.
Use Microsoft 365 data handling maturity levels 2-7-3 to score controls, identify gaps, and plan a practical next improvement.
Use entra id iam audit reports to prove unique identities, MFA, authorization, privileged access, and access reviews for ECC 2-2-3.
Build training records for baseline compliance in two hours with a defensible ISO 27001 6.3 evidence pack for SMB customers.
Build a system administrator software installation training plan that proves secure, approved installs for ISO 27001 surveillance audits.
See which threat intelligence audit evidence siem logs demonstrate collection, analysis, action, ownership, and review for ISO 27001 assessments.
An azure server room access policy template should define who may enter, why, how access is logged, reviewed, and revoked.
What should a board report say about secure office areas: status, business risk, trends, exceptions, and decisions required.
A board dashboard privileged tools report should show control coverage, material exceptions, risk trends, accountable owners, and remediation dates.
Network segmentation audit evidence: the designs, rules, access records, changes, and test results that demonstrate ISO 27001 8.22.
Azure NDA audit evidence should prove signed agreements, review dates, covered parties, and access controls tied to Azure identities.
Use this VLAN segmentation maturity assessment to score your network from ad-hoc to optimized and identify your next ISO 27001 action.
Learn what is split tunneling on a VPN laptop cmmc and how SC.L2-3.13.7 requires full-tunnel remote access.
A security awareness RACI matrix assigns ownership for CMMC AT.L2-3.2.1 training, policies, records, and leadership oversight.
See the cmmc assessor CUI repair ticket evidence needed to prove off-site maintenance equipment was sanitized before release.
Track google cloud data masking kpis for coverage, policy enforcement, access exceptions, audit evidence, and remediation to demonstrate ISO 27001 compliance.
A ransomware policy review postmortem shows how stale access and backup exceptions turned one compromised account into a three-day outage.
Use AWS Artifact physical entry controls evidence—current SOC reports and ISO certificates—to prove AWS data-center access controls to an ISO 27001 assessor.
Vendor vulnerability management requirements 2-10-3 require approved scanning, risk classification, remediation, patching, and trusted vulnerability alerts.
Storage media handling requirements for usb drives require controls for acquisition, use, transport, and secure disposal based on data classification.
Set Windows configuration drift alerts for changes to admin access, security tools, firewall, audit policy, services, and logging.
Use terraform security role assignments to create controlled role allocations, approval records, and repeatable audit evidence for ISO 27001.
Microsoft Sentinel playbook block risky remote sessions by detecting risky sign-ins, revoking sessions, and preserving control evidence.
Build a GitHub Actions CISA KEV daily check that records advisory review, matches affected assets, and opens actionable tickets for SI.L2-3.14.3.
Learn to encrypt company laptops with bitlocker quickly using a one-hour baseline that supports ISO 27001 endpoint-device evidence.
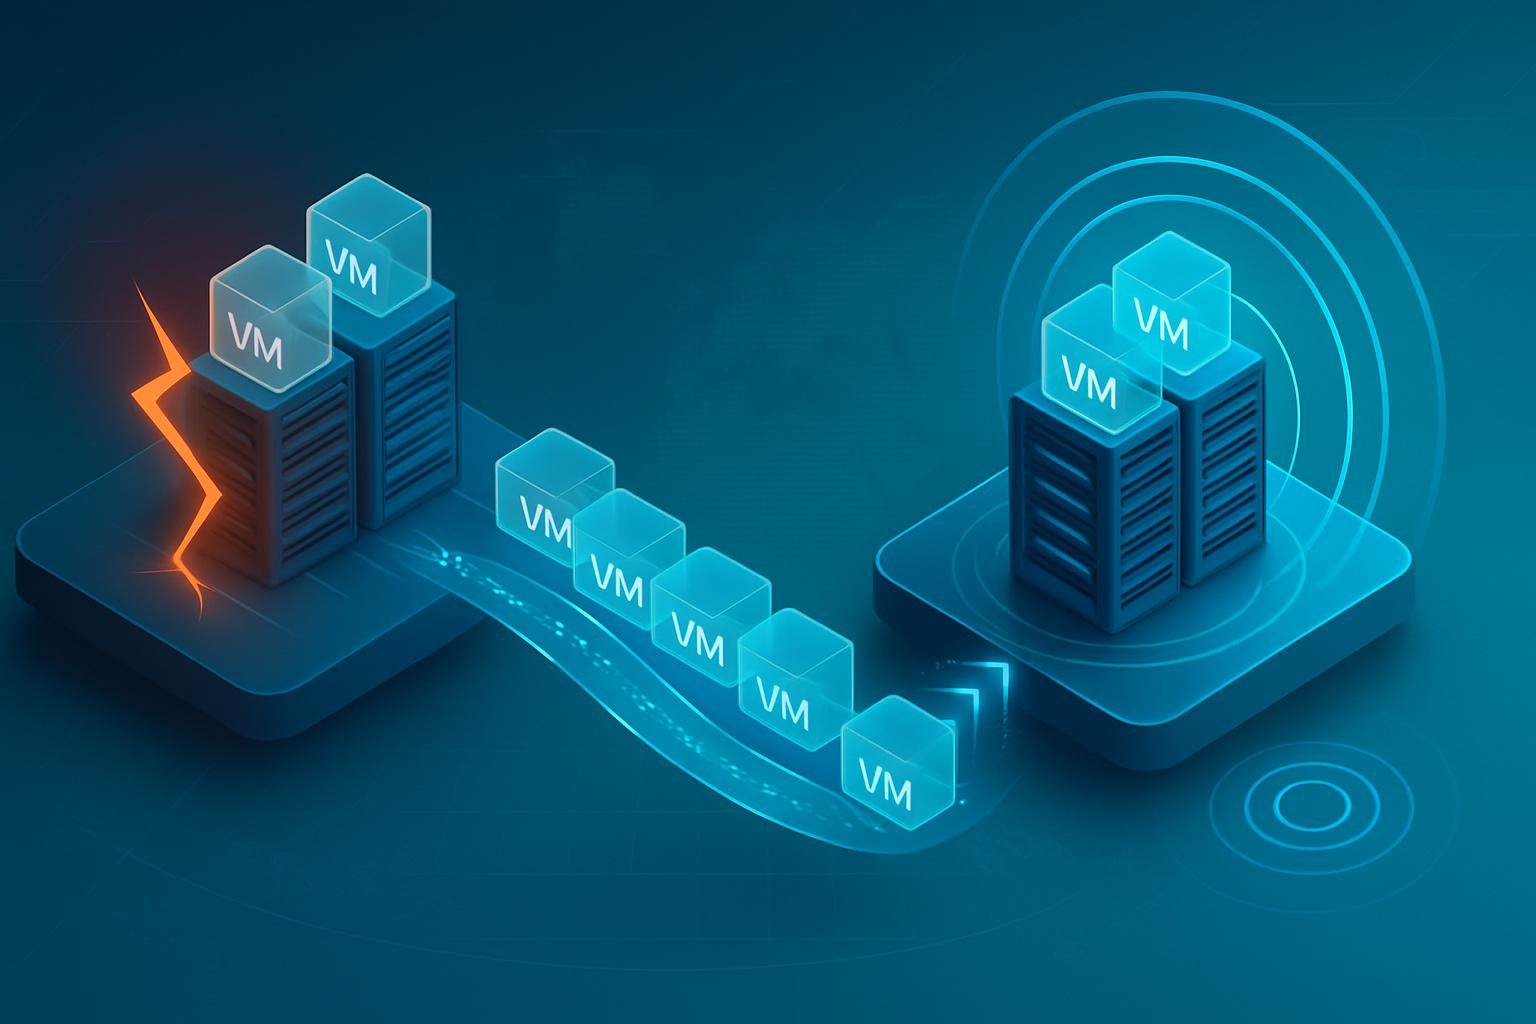
Configure azure site recovery replicate vms disaster recovery settings to maintain recoverable workloads during a regional or physical disruption.
Meet AC.L2-3.1.7 with sudo permissions privileged command audit logs that restrict elevation and preserve traceable evidence.
Use this diagnostic USB media RACI matrix cmmc guide to assign ownership, evidence, escalation, and review duties for MA.L2-3.7.4.
This aws identity federation ultimate guide explains how to implement federated access, MFA, least privilege, PAM, and access reviews for ECC 2-2-3.
Use cmmc account lockout control testing to validate settings, collect evidence, and meet AC.L2-3.1.8 requirements.
Compare risk register vs POA&M for CUI RFPs: use the register to document assessed risk and the POA&M to track approved remediation.
Use this removable media vendor questionnaire template to evaluate supplier controls, score responses, and document MP.L2-3.8.7 evidence.
azure mfa does not end admin sessions; meet MA.L2-3.7.5 by requiring MFA for remote maintenance and closing the connection when work ends.
For nda vs confidentiality clause for contractors, use a signed NDA when access or sensitive information is involved; clauses are not enough.
Use terraform enforce secure application settings through reviewed plans, deployment gates, monitoring, and evidence for ECC 1-6-3.
Use entra id terms of use employee security terms to require, record, and report employee acknowledgement of security responsibilities for ISO 27001.
Follow sql server data masking migration steps to replace direct table access with controlled masked views, test safely, cut over, and validate ISO 27001 alignment.
Learn how to monitor employee security reports in microsoft sentinel with telemetry, alerts, tuning, and incident-response workflows.
Learn to map penetration test findings to remediation tracker with auditable ownership, due dates, retest evidence, and ECC 2-11-3 coverage.
Learn to enable Microsoft Defender for DevOps in Azure and collect ECC 2:2024 1-6-3 evidence for development security reviews.
Microsoft Forms security event report form setup steps for creating a timely ISO 27001 incident reporting channel in Microsoft 365.
Learn how long to keep malware scan logs for cmmc audit: CMMC sets no fixed period; retain verifiable MA.L2-3.7.4 evidence for 12 months.
Use an AWS Audit Manager CMMC ISO 27001 evidence crosswalk to reuse log-analysis evidence across CMMC, ISO 27001, SOC 2, and NIST CSF.
Use hashicorp vault mfa ssh session ttl controls to require MFA for remote maintenance and enforce short-lived SSH access.
Use this google drive source code access audit guide to scope repositories, manage permissions, collect evidence, and test ISO 27001 control 8.4.
does wpa2 authentication count as wi-fi authorization cmmc? Only when approved access is enforced before connection under AC.L2-3.1.16.
Answer: does cloud logging meet cmmc software monitoring requirements? No—pair logs with installation controls, inventory, alerts, and evidence.
Use this CUI media policy template for subcontractors to mark CUI media, state distribution limits, assign ownership, and support MP.L2-3.8.4.
CloudTrail Lake vs CloudWatch CMMC audit review: use CloudWatch for four-hour alerting and Lake for durable investigation queries.
See when can Microsoft Defender replace a SIEM for small IT teams and document SI.L2-3.14.3 without enterprise tooling.
excel vs grc software for cmmc cui risk assessment: a lean, auditable review process for small defense subcontractor teams.
Use azure security awareness policy template key clauses to define training, reporting, evidence, and merger-transition responsibilities for Azure users.
Azure Policy vs Defender for Cloud risk evidence: save policy compliance, security findings, risk decisions, and dated assessment records.
Use this aws shared responsibility cmmc security awareness guide to map AT.L2-3.2.1 risks, responsibilities, policies, training, and evidence.
Are passwords in email compliant cmmc? Usually no: IA.L2-3.5.10 requires passwords to be cryptographically protected in storage and transit.
Are certifications required for cybersecurity analysts? ECC 1-10-4 requires tailored training, professional skill access, and documented evidence.
CUI access screening dashboard KPIs show whether every CUI user was screened before access, where exceptions sit, and what leaders must fix.
Avoid business continuity evidence mistakes by linking approved plans, cyber scenarios, DR tests, ownership, and review records to ECC 3-1-3.
Maintenance technician training CMMC should cover authorized maintenance, patching, change records, access controls, and evidence for MA.L2-3.7.1.
A usb drive policy template should define approved devices, access rules, encryption, transport, disposal, exceptions, and review requirements.
Learn what to test in a microsoft 365 tabletop exercise, including data handling decisions, incident actions, owners, and evidence.
Use this cloud backup vendor due diligence checklist to verify security, recovery, evidence, and contract terms before trusting a provider.
An aws cui repair report for board should show CUI exposure, sanitization evidence, exceptions, risk decisions, and trend metrics.
Track office security kpis BigQuery metrics for access reviews, visitor records, facility issues, and evidence of ISO 27001 control performance.
Export jira maintenance records for cmmc that prove maintenance was planned, performed, reviewed, and retained for assessment.
cmmc emergency access during production outage requires documented, approved, and enforced controls for urgent system changes.
Define logging raci matrix roles so IT, HR, Legal, security, and leaders can assign ownership for producing, protecting, and reviewing logs.
Use this 30 day plan for application security requirements to document controls, test applications, harden releases, and produce ECC 1-6-3 evidence.
Meet incident evidence requirements for small IT team without siem using retained logs, an evidence register, and a lightweight preservation process.
github reports source code access audit evidence shows who can access repositories, what permissions they hold, and how access changes are reviewed.
See how cmmc microsoft defender compliant file scanning meets SI.L2-3.14.5 with defined periodic scans and real-time external-file protection.
Estimate background check cost per employee CMMC at $95–$200 in year one, then calculate the budget, avoided-loss ROI, and buy-versus-build threshold.
Define a cmmc reportable phishing incident and show how to track, document, and notify the right people for CMMC Level 2.
Use contract clauses for 24-hour incident reporting to bind vendors and subcontractors to fast notice, evidence preservation, and audit rights.
Use clear desk kpis to track monthly to prove ISO 27001 clear desk and clear screen enforcement with audit-ready evidence and trends.
Record protection requirements for audit logs require organizations to prevent loss, alteration, unauthorized access, and improper release of evidence.
Cloud vs on-prem sudo audit requirements: compare evidence, logging, retention, and operating tradeoffs for ISO 27001 privileged utility control.
A payroll fraud dual approval postmortem shows why independent review, separated permissions, and audit evidence stop payment diversion.
Azure Key Vault Managed HSM configuration secures high-sensitivity keys with HSM-backed generation, rotation, access control, and ECC 2-8-3 evidence.
Meet CUI subcontractor transfer requirements by authorizing, encrypting, documenting, and enforcing every approved CUI data flow.
siem vs ids for small business: start with a managed SIEM for broad monitoring, then add IDS when network-specific detection is needed.
Security training vs policy acknowledgment: AT.L2-3.2.2 requires role-specific skills, not just a signed policy, to prove staff can perform assigned duties.
Understand microsoft defender alert vs incident: close benign Defender detections, document true incidents, and meet CMMC IR.L2-3.6.2 reporting.
Rippling vs BambooHR disciplinary case pricing by company size: compare costs, audit evidence, and the best ISO 27001 fit.
Use a powershell script to enforce bitlocker on remote laptops, escrow recovery keys, and produce ISO 27001 remote-working evidence.
Use this powershell script policy template to authorize, restrict, monitor, and document PowerShell use for CMMC Level 2 assessments.
An offboarding vs role transfer security checklist distinguishes account closure from access redesign while preserving ISO 27001 evidence.
A practical ISO 27001 playbook to migrate excel asset list to compliant asset register, assign owners, preserve evidence, and validate control 5.9.
Use Google Cloud Identity to cloud identity suspend user after policy violation, revoke active sessions, and retain audit evidence for ISO 27001.
Configure cloud identity 2-step verification remote mfa by enforcing 2SV for remote-access users and retaining ISO 27001 evidence.
Learn how to create a 30 day employee exit plan with a practical migration path, cutover runbook, evidence, and ISO 27001 controls.
Use azure monitor outsourced developers activity log to export, alert on, and retain contractor Azure changes for ISO 27001 8.30 evidence.
Build a Google Workspace mobile device compliance dashboard with KPI targets, data sources, and reporting evidence for CMMC AC.L2-3.1.18.
Learn how to automate entra named locations powershell with idempotent Microsoft Graph scripts, approvals, logging, and rollback controls.
Use an azure authority contact maturity assessment to score ISO 27001 A.5.5 processes and plan the next 90 days of improvement.
Google workspace nda requirements: document, sign, review, and retain confidentiality agreements for users who access sensitive information.
Use this google workspace audit log timestamp clause template to require synchronized audit timestamps from subcontractors supporting CMMC Level 2 work.
google cloud vs on prem session lock audit evidence: compare enforceable settings, proof sources, and tradeoffs for CMMC AC.L2-3.1.10.
Use GitHub Actions scan test tool ZIPs before USB release with malware checks, hashes, signed evidence, and a controlled approval gate.
How an exposed Docker API crypto mining incident happens, what CM.L2-3.4.7 requires, and the practical fixes that prevent recurrence.
Does microsoft 365 include clock synchronization? No—learn the incremental cost, ROI, and budget for AU.L2-3.3.7 compliance.
Use defender for cloud CUI risk assessment evidence to document recurring RA.L2-3.11.1 risk reviews, decisions, and remediation.
Compare CUI notice software pricing by company size, including 10 vendor options for NIST 800-171 AC.L2-3.1.9 system-use notices.
Learn how to create employee security terms in entra id, require acceptance with Conditional Access, and collect ISO 27001 audit evidence.
cloud vs on-prem antivirus costs small defense contractor: compare SI.L2-3.14.5 licensing, operations, scan evidence, and deployment choices.
Calculate build vs buy usb device control total cost of ownership, 3-year payback, and a defensible AC.L2-3.1.21 budget.
An azure storage sas link cui disclosure postmortem showing how weak SAS and TLS controls exposed CUI and how to correct SC.L2-3.13.8 failures.
CMMC guest account inactivity requirements require guest identifiers to be disabled after a defined period without use.
Avoid google cloud security review mistakes that weaken independent oversight, audit evidence, and risk decisions across your GCP environment.
Secure equipment siting meaning for Azure admins: protect the devices and locations that support Azure services under ISO 27001 7.8.
This azure offboarding incident postmortem shows how a missed role removal left production access active and what controls prevent recurrence.
Learn why an unassigned USB bypassed Intune, exposed CUI, and the intune unowned usb breach lessons learned needed for MP.L2-3.8.8.
Use google workspace rfp cabling security questions to evaluate providers against ISO 27001 7.12 cabling protection requirements.
Configure Google Docs eSignature employment security terms workflows to document acceptance of ISO 27001 information-security responsibilities.
Use GAM add approved users to Google Workspace groups from a screening-approved roster with auditable checks for CMMC PS.L2-3.9.1.
Use Google Cloud KMS destroy encryption keys before repair to make CUI on encrypted equipment inaccessible before off-site maintenance.
Wi-Fi 802.1X authentication ultimate guide for implementing mutual wireless access controls and evidence for CMMC SC.L2-3.13.15.
This web filtering dns filters ultimate guide explains how to reduce malicious website exposure, implement controls, and evidence ISO 27001 compliance.
This network cable security ultimate guide explains how SMBs protect power and data cabling for ISO 27001 audit evidence.
Cmmc manual log review vs mdr: MDR can monitor alerts, but it does not replace reviewing and updating logged event types for AU.L2-3.3.3.
Use a 30-day, evidence-driven process to move from no incident plan to SaaS incident response playbook readiness for enterprise reviews.
A step-by-step plan to migrate web server TLS to FIPS validated cryptography, validate modules, cut over safely, and retain evidence.
A phased playbook to migrate shared sudo access to break glass accounts with audit evidence, rollback steps, and ISO 27001 controls.
Learn how to fix missing incident response procedures audit finding with scoped playbooks, proof of use, ownership, and review evidence.
Use a WDAC block unauthorized apps CMMC quick start to enforce a documented deny list and collect CM.L2-3.4.8 evidence in four hours.
Learn how to block legacy authentication in Microsoft 365 Entra Conditional Access with a tested policy, verification steps, and assessor evidence.
Use this google workspace maintenance log policy template to document maintenance, ownership, evidence, and review requirements for MA.L2-3.7.1.
Google Admin wipe vs Powerwash CUI repair: choose remote wipe when online, document local resets, and prove MA.L2-3.7.3 with simple records.
github enterprise cloud vs server secure code reviews: choose Cloud for lower operational burden or Server for strict isolation and controlled hosting.
Yes. A ransomware scenario cui risk assessment helps demonstrate periodic, documented risk review for CUI systems under RA.L2-3.11.1.
google cloud vulnerability management compliance myths 2-10-3: what ECC 2-10-3 requires beyond scanning and patching.
Configure these settings to combat stalkers, spammers, and everyone else annoying you on WhatsApp.
If configured correctly, during a disaster a smartphone can be more than a communication device.
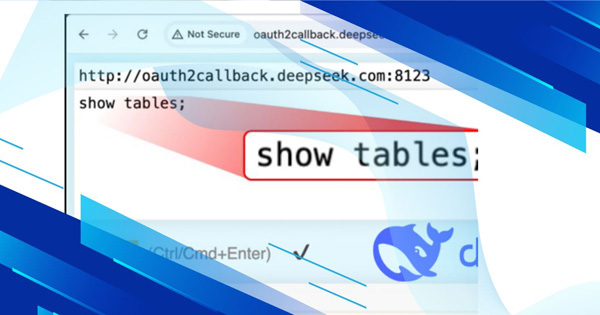
DeepSeek AI database security flaw uncovers confidential keys, chat records, and backend information, providing unfettered access to the entire system.
The Russian hacker group Star Blizzard posed as U.S. government officials in fraudulent emails, urging recipients to join a WhatsApp group supposedly dedicated to showcasing "the most recent non-governmental initiatives supporting Ukrainian NGOs."
The Biden administration aims to enhance digital security for both the government and private sector in the United States through the implementation of this executive order.
The arrest of the Telegram founder seems to have caused concern among those who use the platform for child exploitation, as it has had a notable impact.
A Volkswagen subsidiary data breach has exposed the location and other information of 800,000 electric vehicle owners for several months.
US Army soldier shared on the Telegram messaging service that they had breached the security of over 15 telecom providers through hacking.
Hackers supported by the Chinese government successfully penetrated the Treasury Department's computer security protocols, as stated in a letter sent to lawmakers.
Designate between two and four global administrators to ensure effective management and security within your Microsoft 365 environment.
Secure your Microsoft 365 environment by ensuring administrative accounts are distinct and solely cloud-based, enhancing control and minimizing risks.
Secure your Microsoft 365 environment by ensuring administrative accounts are distinct and solely cloud-based, enhancing control and minimizing risks.
According to a survey conducted by Kaspersky Labs, only 10% of employees are diligent in safeguarding work-related information on their personal devices.
Data breaches have become increasingly common, leading many organizations to establish comprehensive policies for handling them. In 2015, Anthem Blue Cross Blue Shield, a prominent US health insurance provider, disclosed a significant breach, revealing that approximately 78.8 million Social Security records and other sensitive personal data had been compromised. We look at four stages of containing a data breach.
Penetration testing is a highly effective method for evaluating your organization's existing cyber security measures (ISO 27001, NIST SP 800-171, HIPAA). Here are 5 crucial reasons to conduct a penetration test
Placing phones in a microwave prevents hacking?
Telehealth, what is it? how does it work? Telehealth explained.
An In-depth Look at Cybersecurity in the US Healthcare Industry through Facts and Statistics
Learn how we configured a client's Microsoft 365 environment to meet NIST SP 800-171 requirements and moved their on-premise resources to the Microsoft 365 environment
Learn how our Azure AD services can streamline and secure your IT environnment.
How we helped a regional logistics company access historical data and provide the tools to mine it for information
How we helped a small business increase their sales by six figures and in salary cost using a custom built email marketing automation platform
Learn how our policies and procedures service enabled a customer to earn two cybersecurity accreditations.
Learn how we helped a DoD contractor meet compliance requirements by securing their Microsoft 365 tenant.
Using a security frame helps an organization establish and meet its security objectives.
Cyber buzzwords always get thrown around causing confusion for readers.
Which of these top 5 cybersecurity certifications do you have?
Having trouble with data classification in your small business? Here are three classification labels you can use.
Perform these tasks to greatly improve cybersecurity at a small business.
Follow my tips on how to pass the CISSP exam.
To meet NIST SP 800-171 requirements you must create and maintain a system security plan (SSP).
Organizations should have standardized procedures for responding to incidents, use this incident response checklist next time you respond to an incident.
Every system security plan should include or reference a hardware and software inventory.
Learn what a collaborative computing device is and how to meet your NIST SP 800-171 and CMMC requirements.
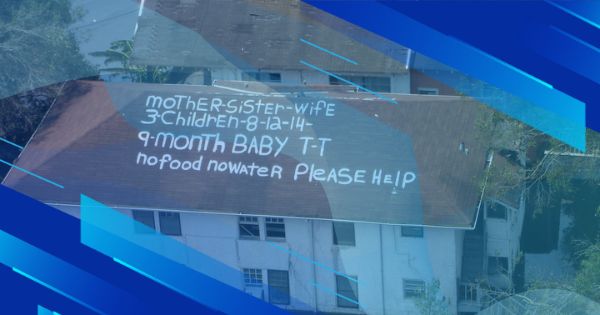
Are you preparing for a natural disaster, civil unrest, nuclear holocaust, or zombie apocalypse? If so, you need a digital bug-out bag.
When traveling or crossing through border controls there are a few cybersecurity tips and best practices you should follow.
Learn how to clean up your online presence and stay anonymous.
Classifying and labeling data is a critical part of any mature cybersecurity program.
Is cybersecurity spelled as one word or two? The answer is it depends...
Employing the principle of least functionality is critical for organizations seeking to reduce their cyber risk.
The term cyber security is often heard in the media, government circles, and the information technology community. Is the term being used incorrectly?
In 1903 the world’s first hacking incident occurred, marking the start of an era. At the Royal Academy of Sciences in England, Nevil Maskelyne pulled off an unharmful yet very embarrassing hack.
Using free and open-source software (FOSS) to meet your cybersecurity needs is a great way to improve your organization’s cybersecurity posture without emptying your wallet. Here are 5 open source cybersecurity tools your company can leverage.
Although an operational necessity, allowing employees to work from home increases cyber risk. We cover six cyber risks and offer mitigations.
Laptops supplied to British schools by the Department for Education came preloaded with malware. Yes you read that right...
The Signal Messenger App is rising in popularity. Here are some common questions people have about it.
Tackling cybersecurity challenges is no walk in the park. However, you can use these five simple actions to improve cybersecurity at your organization.
More than 34% of businesses around the globe are affected by insider threats yearly.[1]
Malvertising is a serious threat that can often be overlooked. Ad blockers can help mitigate this threat.
We are used to locking down workstations and servers however we often overlook printers. Here is how to secure your printers.
Want to help save the environment and improve your information security? Then go paperless.
Small businesses are often the target of cyber attacks. Why don't they take cybersecurity as seriously as they should?
Training employees on cybersecurity practices and reminding them of security threats is paramount for any successful program.
Everyone can agree that breaking the rules should have its consequences but is punishing users for cybersecurity policy violations and mishaps a good idea?
Our data may be stored digitally but fundamentally it is still very much linked to the physical world. Here is how to bolster cybersecurity through physical security.
What is split tunneling as it relates to virtual private networks? Is using split tunneling secure? How does it impact CMMC compliance requirements?
What is FIPS 140-2? Why was it created? Which encryption algorithms are FIPS 140-2 compliant?
Tired of Silicon Valley and the Government tracking your every move? Use these free apps and services to help protect your privacy.
Use these tips to protect your home from cyber threats.
Does requiring users to reset their passwords every few months promote better security or does it reduce security?
Separating the duties of employees and implementing the principle of least privilege is vital to any cybersecurity program but what is the difference between the two?
Privacy and security are related but what is the difference?
Does hiding your SSID improve security?
Does a Mac need antivirus? A lot of people believe that Macs don’t need it. Where did this belief come from? Is it true?
We discuss business impact analysis definition, steps, and provide templates from NIST.
Knowing how to choose the right multi-factor authentication (MFA) solution to meet your company's compliance and security needs can save you a lot of time down the road.
Check out these useful cheat sheets for cybersecurity tools like NMAP, Wireshark, and more!
The occurrence of a cybersecurity incident isn’t a matter of if but when. Organizations need to have incident response plans in place. So what is an incident response plan?
The NIST Privacy Framework provides organizations with a tool to manage privacy risks. How can it benefit your organization?
By revoking administrator rights from a Windows system you can remediate 94% of vulnerabilities affecting the Windows operating system. Here’s how.
A brute force attack uses trial and error to guess login information such as passwords with the hope of eventually guessing it correctly.
In short, SSL is the now deprecated predecessor of TLS.
Malware is a broad term for any type of harmful software designed to exploit a device, service or network.
Social media can help you connect with friends and family, it can also be a way for bad actors to connect with you.
A patch and vulnerability management program is one of the most important parts of any cybersecurity program. In this post I explain how to build one.
Browser extensions can increase productivity, however, left unmanaged they can create security risks for your organization.
Here are the top 5 most shocking phishing statistics.
Your employees can receive some of the same training as Pentagon employees at no cost to you.
Continue reading to find out how to prevent hackers from taking over your phone.
Learn to how to secure your twitter account to avoid being hacked.
Here are the top small business cybersecurity statistics you need to know.
Companies often overlook the basic elements of cybersecurity, leaving them vulnerable to attack.
Here are the top 10 recent cybersecurity statistics you need to know for 2020.
77 percent of corporate end-users surveyed have used personal flash drives for work-related purposes.
A system security plan (SSP) lists an organization’s cybersecurity requirements and explains how it meets them. We will show you how to create your own SSP!
The Defense Information Systems Agency (DISA) has a wide range of security technical implementation guides (STIGS) company’s can leverage to secure their IT systems.
Did you know that 42% of used drives sold on eBay hold sensitive data?
Creating an acceptable use policy for your information system is a good way of informing users of your security policies and limiting legal risks.
Change control procedures are the backbone of any mature cybersecurity program. We offer a list of items IT teams should consider before deploying changes to their production environment.
Understanding what an information system is and its components is critical to effectively implementing your company’s CMMC requirements.
America will protect its defense industrial base from cyber attacks with a new cybersecurity framework and an army of assessors.

Talk with our team about your framework, your gaps, and the right plan.
Get a demo